A network security pitch in Metro Detroit usually starts backwards. A sales rep sits down in your conference room in Troy or Southfield, slides a laminated diagram across the mahogany table, and tries to sell you an eight-layer software stack before asking how many warehouse doors have badge readers on your local subnet.
Most businesses between 20 and 250 employees do not need a twenty-four-hour enterprise security operations center with three rotating shifts. They need clear visibility, basic network segmentation, working backups that restore cleanly on a random Tuesday morning, and an engineer who actually patches the firewall firmware on schedule. In the contract reviews we run out of Royal Oak, we see the same pattern constantly. Companies pay five figures a month for security tools configured once in October three years ago and never touched since.
Here is what real network security work looks like, what it costs across Southeast Michigan, and how to tell if an IT provider is selling you genuine protection or just padding their monthly recurring revenue.
What Network Security Actually Entails (Beyond the Firewall Box)
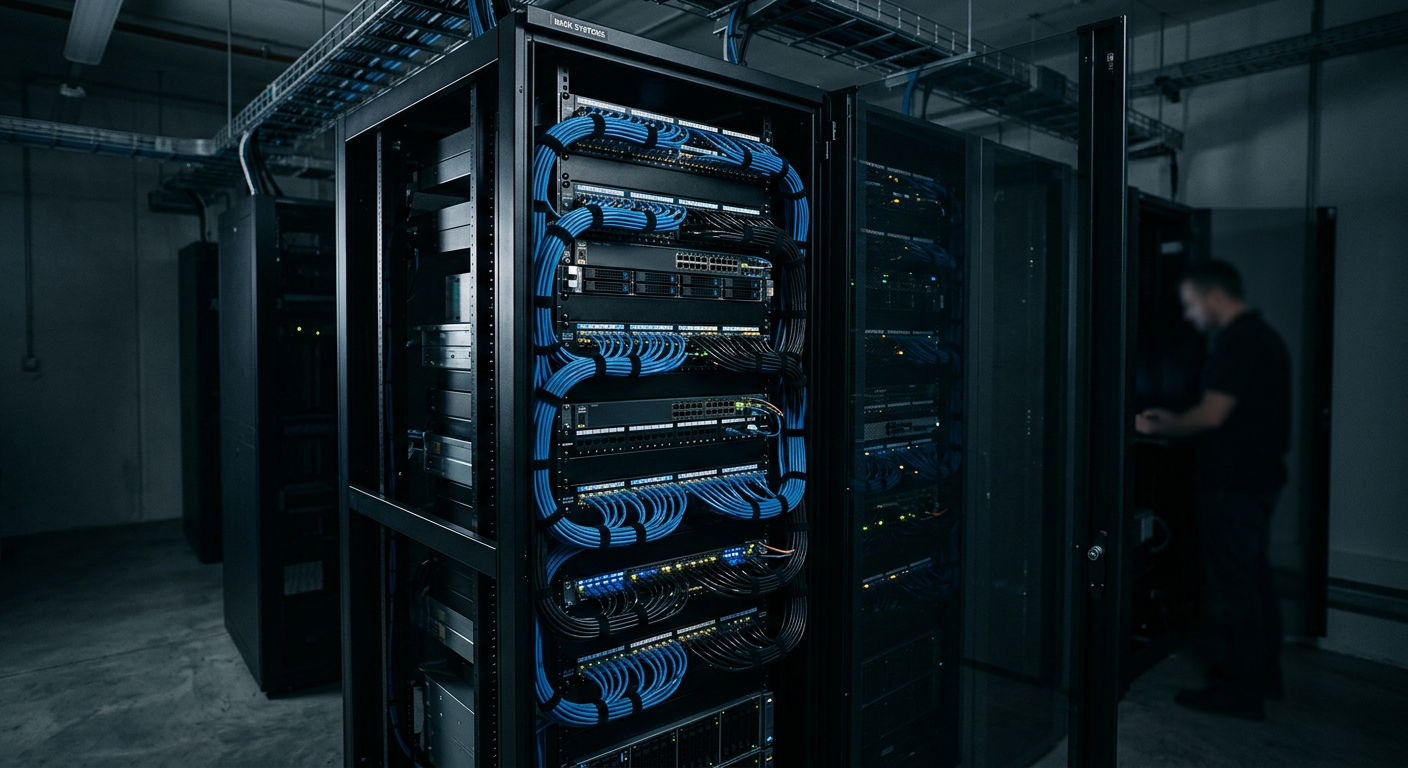
Network security is not a blue appliance bolted into a server rack in the basement. It is the boring, daily operational discipline of keeping unauthorized traffic off your systems while letting your staff do their jobs without constant headaches.
When we audit network environments for Detroit IT services clients, real network security breaks down into four operational buckets:
- Perimeter and Edge Control: Modern firewalls, secure remote access, and zero-trust policies that replace old, unmonitored point-to-point VPN tunnels that let any compromised laptop walk right onto your main subnet.
- Internal Segmentation: Keeping your office printers, guest Wi-Fi, HVAC controllers, and shop-floor CNC machines strictly isolated from the accounting database and payroll records.
- Continuous Monitoring and Endpoint Response: Lightweight agents on every laptop and server flagging abnormal behavior, backed by human engineers who pick up the phone when an alert fires at two in the morning on a holiday weekend.
- Identity and Access Management: Enforcing phishing-resistant multi-factor authentication across email, ERP software, and server consoles, alongside an offboarding process that kills former employee credentials within sixty minutes of departure.
If a provider hands you a proposal that focuses entirely on selling you new hardware without mentioning identity controls or subnet isolation, they are clearing out their distributor inventory. That is not protection. Our cybersecurity and risk advisory focuses on building controls that map to real operational risks rather than vendor sales quotas.
What Detroit Businesses Pay for Network Security
Pricing in Southeast Michigan varies wildly depending on whether you buy standalone network security or bundle it into a broader managed IT agreement.
For standalone managed detection and response (MDR) or managed security services, expect monthly costs between $35 and $85 per user per month. The wide spread depends on whether the provider includes live remediation when malware hits, or simply forwards you an automated email alert and tells your internal staff to clean up the mess.
When network security gets bundled into a full managed service provider (MSP) agreement, total pricing across Metro Detroit typically lands between $125 and $250 per user per month. The low end usually covers basic endpoint protection, web filtering, and firewall patch management. The high end includes regular vulnerability scanning, managed backups, threat hunting, and compliance documentation for regulators or insurance carriers.
Hardware is almost always billed separately. A solid business-grade firewall for a 50-person office runs between $1,500 and $4,000 upfront. Recurring security subscription licenses for that unit will cost between $800 and $2,200 annually. Keep an eye on those license renewals: we frequently see providers mark up hardware subscription pass-throughs by 30% to 40% above standard list price.
Industry Demands Across Southeast Michigan
Network designs cannot come out of a cookie cutter. A law firm in Birmingham has entirely different operational risks than a Tier-2 automotive supplier in Warren.
Manufacturing and Mobility Plant networks are notoriously fragile. We routinely walk manufacturing floors where twenty-year-old stamping presses, paint booths, or coordinate measuring machines run on unsupported versions of Windows because the machine vendor went out of business or demands $80,000 for a software upgrade. You cannot install modern endpoint protection on those controllers without crashing the line. Network security in these facilities means strict air-gapping: isolating operational technology (OT) from the corporate network so an employee opening a malicious email attachment in the front office cannot halt the production shift.
Healthcare Practices and Clinics Medical practices in Wayne, Oakland, and Macomb counties handle protected health information under strict federal guidelines. Clinics must separate diagnostic imaging gear, guest Wi-Fi, and electronic health record databases. Encrypted Wi-Fi, audit logging on patient chart access, and automatic session timeouts are the baseline. If an unmanaged tablet on the guest network can reach the billing server, that is an immediate compliance failure.
Professional Services and Real Estate Accounting firms, engineering groups, and commercial real estate brokerages manage wire transfers and valuable client files. Their primary risk is rarely an external port scan from a foreign state actor. It is business email compromise. Network defense for these firms centers on conditional access policies, device health verification, and aggressive email filtering that catches spoofed escrow instructions before money leaves the bank account.
Do you know what happens to your network traffic when your team works from home or a job site? If your answer is "they connect to a VPN and hope for the best," you have a blind spot that standard antivirus software will not catch. Remote machines need device health checks before they are permitted to touch internal file shares.
How to Spot a Provider Selling Overhead Instead of Protection
Many providers pitch complex, multi-layered security stacks because more software line items justify higher monthly retainer invoices. But stacking five tools that generate hundreds of unread alerts does not make you safe. It just makes your IT team exhausted.
Watch out for these red flags during vendor meetings:
1. Proprietary Hardware Traps: The provider insists on deploying obscure firewall hardware that only their staff can administer. If you ever decide to change IT vendors, they take the admin keys or brick the box, holding your network hostage. 2. The Annual "Set It and Forget It" Audit: They run a flashy network assessment during the sales pitch to win your business, but the contract includes zero ongoing vulnerability testing or quarterly configuration reviews. 3. Zero Standards Alignment: The provider cannot explain how their architecture maps to established frameworks like the NIST Cybersecurity Framework. Good network security relies on recognized engineering standards, not a homebrewed recipe cooked up by a local sales team. 4. Silence on Cyber Insurance Underwriting: As we break down in our guide on cybersecurity questions your insurance carrier will ask, insurance underwriters now demand specific network configurations before binding coverage. A capable provider aligns your infrastructure with those underwriting criteria proactively.
To see how we separate reputable engineering shops from aggressive sales organizations, read our practical guide on how to choose an IT provider in Metro Detroit.
The Questions That Separate Real Engineers from Sales Reps
Before you sign a three-year network security agreement, bring these four questions into the room:
- "Who actually responds when an intrusion alert triggers at 11:00 PM on a Friday, and what is your guaranteed response time in writing inside the SLA?"
- "How do you handle micro-segmentation between our operational shop equipment and our corporate workstations?"
- "If we part ways in two years, do we own the network firewalls, switches, and administrative configurations outright, or do you take them?"
- "Can you provide executive reporting on open vulnerabilities that our leadership team can understand, rather than dumping raw 70-page automated scan logs on my desk?"
A competent IT firm will give you direct, plain-English answers on the spot.
FAQ
What is the difference between network security and cybersecurity? Cybersecurity covers your entire digital footprint: user identities, cloud applications, email security, and staff awareness training. Network security is the specific engineering discipline focused on the physical and virtual pathways: the routers, switches, firewalls, Wi-Fi access points, and the data packets flowing between them.
How often should a small or mid-sized business run vulnerability scans? Vulnerability scans should run automatically on a weekly or monthly schedule, paired with a human review at least once a quarter. Organizations can also use free baseline assessments through CISA cyber hygiene services to audit their public-facing IP addresses and external firewalls.
Can our internal IT person handle network security alone? Almost never once an organization grows beyond 30 or 40 employees. A single internal IT professional spends their week resetting passwords, swapping out failing docks, onboarding new hires, and troubleshooting ERP glitches. Dedicated network defense requires continuous log monitoring, specialized toolsets, and engineers who monitor emerging exploit trends every day.
Sources
- NIST Cybersecurity Framework - Core standards and guidance for managing organizational cybersecurity risk.
- CISA Cyber Hygiene Services - Federal vulnerability scanning and testing resources available to organizations.
If you want a second set of eyes on your existing network security agreements, an upcoming MSP renewal, or a stack of hardware quotes, book a free 15-minute review with Good Wolf Technology. We review your current contracts and network design without sales pressure or vendor bias.